AI SOC Analyst

Every alert investigated before an analyst opens it.

RubyCyber is an autonomous Tier-1 analyst that lives inside the SIEM, EDR and SOAR you already run. It triages around the clock, reaches a verdict with its reasoning attached, then runs the playbook.

Self-serve sign-up  /  Windows agent  /  cloud or local AI
app.rubycyber.xyz
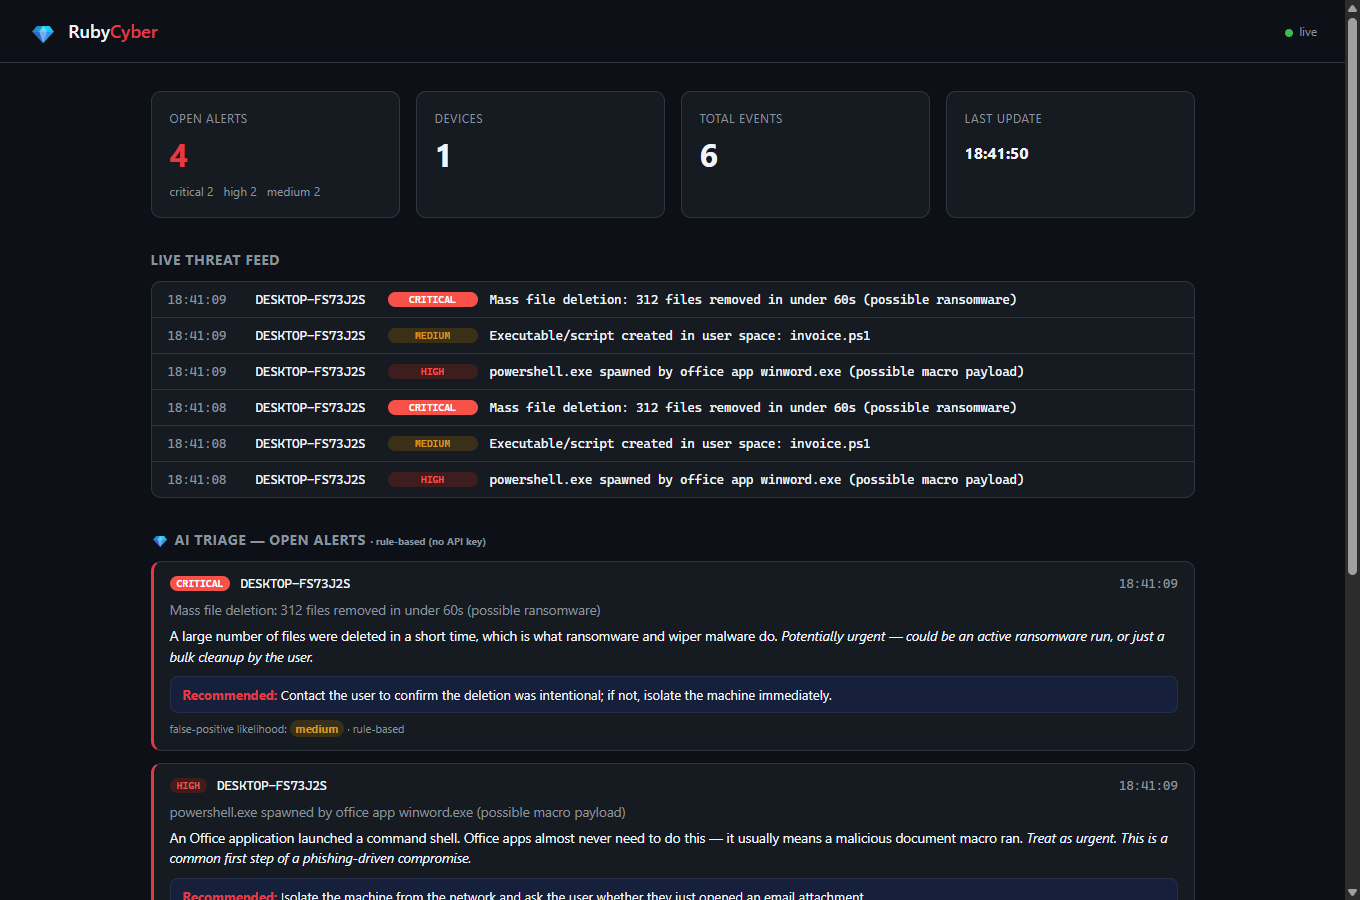
RubyCyber console: live threat feed and AI triage verdicts
Live console. Every alert triaged to a plain-English verdict with a recommended action. Here, running fully on a local model, no data leaving the building.
▸

Watch it investigate. No sales call.

A real alert lands. This is what your team sees seconds later.

rubycyber · live investigation▸ replay
› alert ingested · source: microsoft-sentinel · incident #4827
  WINWORD.EXE → powershell.exe -enc SQBFAFgA…
› investigating…
✓ pulled the process tree from the EDR · Word has no business spawning a shell
✓ decoded the command line · base64 → obfuscated downloader
✓ matched threat intel · C2 domain seen in active campaigns
✓ checked the user baseline · j.doe has never run PowerShell
✓ scoped blast radius · 1 host, no lateral movement yet
✓ mapped to MITRE ATT&CK · T1566 phishing → T1059.001 PowerShell
› verdict: TRUE POSITIVE · high · confidence 96%
› recommended playbook: isolate_host + reset_credentials
approve & runescalate
› running playbook · isolate_host + reset_credentials
✓ DESKTOP-7F2A isolated from the network
✓ j.doe credentials reset, sessions revoked
› incident #4827 closed · resolved in 38s, no analyst touched it
› escalated to Tier-2 · assigned to on-call analyst
✓ full timeline + evidence attached to the ticket
› analyst opens to a finished investigation, not a raw alert
Click a decision above to see the playbook run.
01

An analyst that never clocks out.

No new platform to learn. RubyCyber reads from the tools you already trust and works the queue while your team sleeps.

Sign up

Download the agent

Create an account, install the Windows agent, and link it to your tenant in minutes. Running a SIEM or EDR too? Connect it for fuller context.

Investigate

It reasons through every alert

Pulls context across your tools, follows the evidence like a Tier-1 analyst, and reaches a verdict, confidence and all.

Resolve

Verdict, then the playbook

Real threats arrive with a one-click decision; noise is closed out. Approve, and your SOAR playbook runs.

02

It does the analyst's work, and shows it.

Not a chatbot bolted onto a dashboard. An investigator that reaches conclusions, with the reasoning attached so your team can trust them.

Verdict

Plain-English, with evidence

True or false positive, severity, scope, and the exact next step, backed by the artifacts it pulled. It shows its work, so analysts believe it.

Signal

Separates real from noise

Correlates endpoint, identity and network to surface the intrusions hiding in the ~90% of alerts that are false alarms.

macro → shellcredential theftlateral movementdata exfil

Response

Runs your playbooks

Hands the matching SOAR playbook a one-click trigger, or waits for approval. You keep your finger on the button.

Scale

Built for managed SOCs

Multi-tenant from day one. One analyst across every client an MSSP protects. The leverage a managed SOC actually needs.

▸

What it handles while you sleep.

Phishing macro

Word spawns a shell at 2 a.m.

RubyCyber decodes the payload, confirms it's live, and isolates the host before it beacons out. Your team wakes to a closed incident, not a breach.
Ransomware

Hundreds of files deleted in seconds

Recognized as a wiper/ransomware pattern and contained in seconds, with the affected host and user already scoped.
Insider risk

Unusual data transfer off a finance laptop

Flagged with the user, the destination and the volume. A verdict an analyst can act on, not a raw log line.
Alert fatigue

1,000 alerts overnight

980 closed as noise, 20 escalated with reasoning attached. Your analysts start the day on the 20 that matter.
Your data stays home

The only AI analyst that can run entirely inside your own environment.

Cloud Copilots ship your most sensitive telemetry to a vendor. RubyCyber can run its model locally. Your logs, alerts and evidence never leave the building. Same structured verdict, zero egress.

// same verdict, cloud or local
{
  "alert":    "WINWORD.EXE → powershell.exe",
  "source":   "microsoft-sentinel",
  "verdict":  "true_positive",
  "severity": "high",
  "confidence": 0.96,
  "playbook": "isolate_host",
  "engine":   "local:llama3.2"
}
Connects to the stack you already run
Microsoft SentinelSplunkCrowdStrikeDefenderSentinelOneTorqTinesCortex XSOARJiraServiceNowSlack
03

Priced like a teammate.

Sign up, download the Windows agent, and you are live in minutes. Cloud AI usage is included; or run a local model (Ollama) at no AI cost.

Team
Per seat
For internal SOCs getting started.
  • Windows agent, self-serve
  • Autonomous Tier-1 triage
  • Cloud AI usage included
  • Verdicts in Slack / Teams
Get started
MSSP
Per tenant
For managed SOCs and MSPs.
  • Multi-tenant, unlimited clients
  • SOAR playbook execution
  • Cloud AI included, or local (Ollama)
  • White-label reporting
Get started
Enterprise
Custom
For large or regulated environments.
  • On-prem / VPC deployment
  • SSO, audit, data residency
  • Custom integrations & SLA
Talk to us

Give your SOC an analyst
that never sleeps.

Get started